AI security
An AI agent needs clear boundaries.
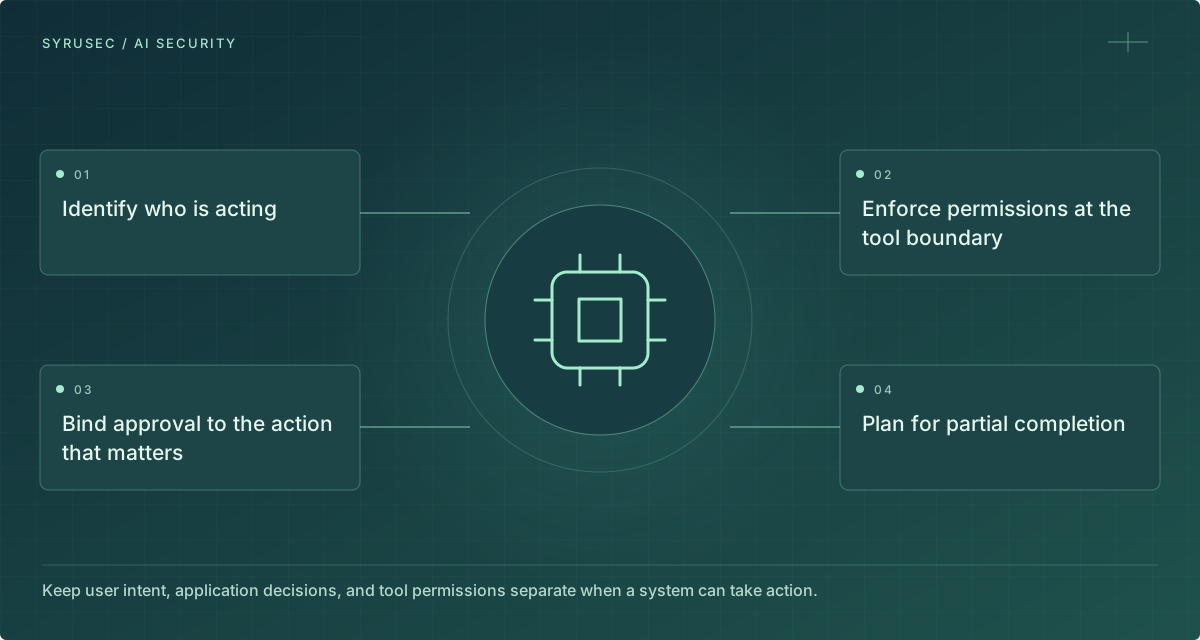
Keep user intent, application decisions, and tool permissions separate when a system can take action.
Read and explore ↗ SyruSecAI GOVERNANCE · RISK · SECURITY
LEARNING PATH
Explore prompt injection, retrieval permissions, agents, and AI-enabled attacks.
An AI application combines familiar software risks with new ways for content to influence behavior. Look at the complete system: identities, documents, tools, credentials, outputs, and external services. The most useful controls remain enforceable even when a model makes an unexpected choice.
You do not need to read everything in order. Choose a question that resembles your work, follow the guide, and try the exercise with a fictional example or an authorized review of your own systems.
A SUGGESTED ROUTE
Prompt injection makes the boundary between useful information and trusted instructions difficult to maintain.
Retrieval-augmented generation creates new paths to existing information. Preserve permissions along those paths.
Keep user intent, application decisions, and tool permissions separate when a system can take action.
Understand how AI supports attackers and authorized testers without confusing a demonstration with a reliable autonomous capability.
AI security
Keep user intent, application decisions, and tool permissions separate when a system can take action.
Read and explore ↗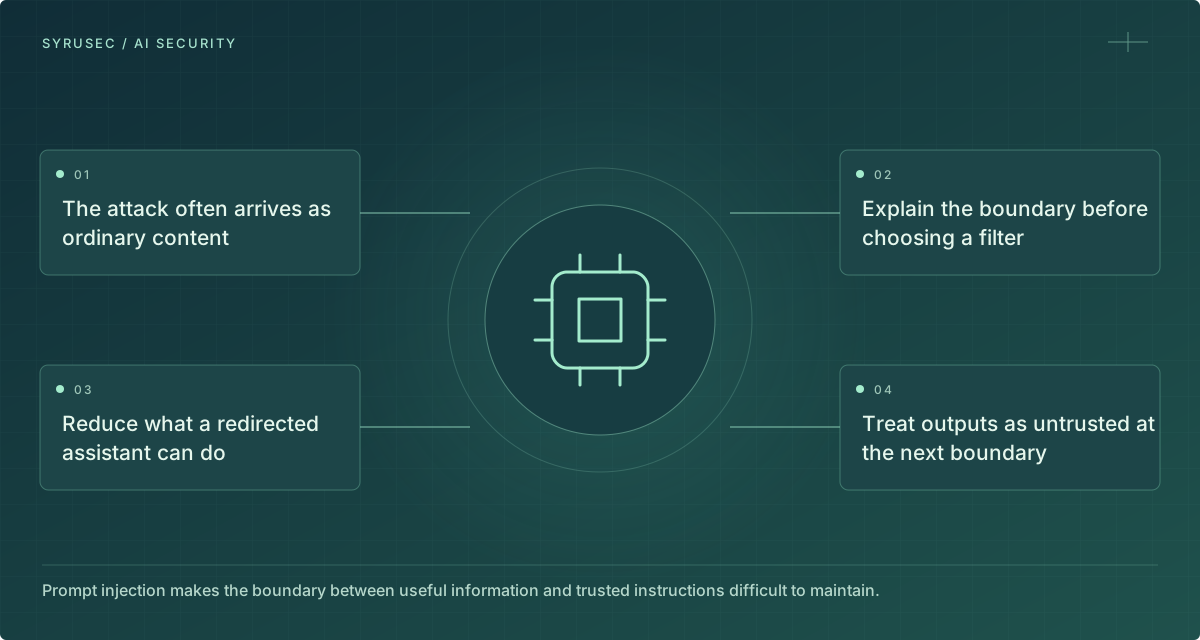
AI security
Prompt injection makes the boundary between useful information and trusted instructions difficult to maintain.
Read and explore ↗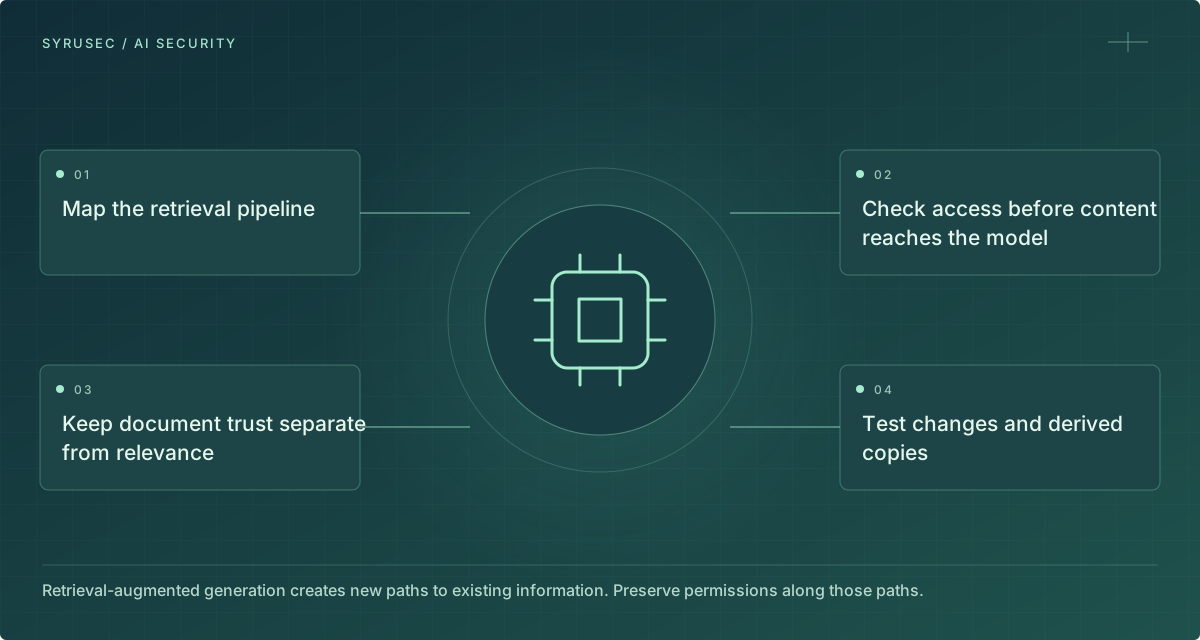
AI security
Retrieval-augmented generation creates new paths to existing information. Preserve permissions along those paths.
Read and explore ↗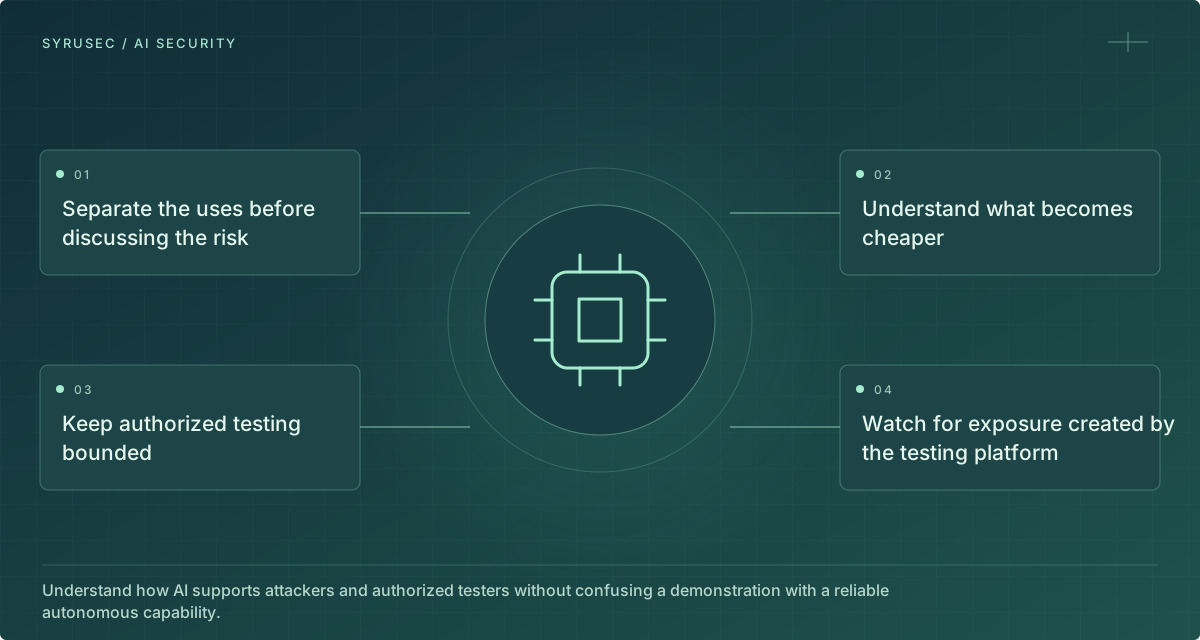
AI security
Understand how AI supports attackers and authorized testers without confusing a demonstration with a reliable autonomous capability.
Read and explore ↗